

Before you begin
You need:- an active Aion organization;
- a visible Project with an MCP-capable Ion, or an eligible global MCP server;
- the permissions required by the server you want to use.
Browse MCP servers
Choose Project or Global
The catalog separates servers by where they are available:
Project MCP configuration remains read-only on this page. To change which tools are allowed or blocked, edit the
Ion’s MCP capability configuration in Composer.
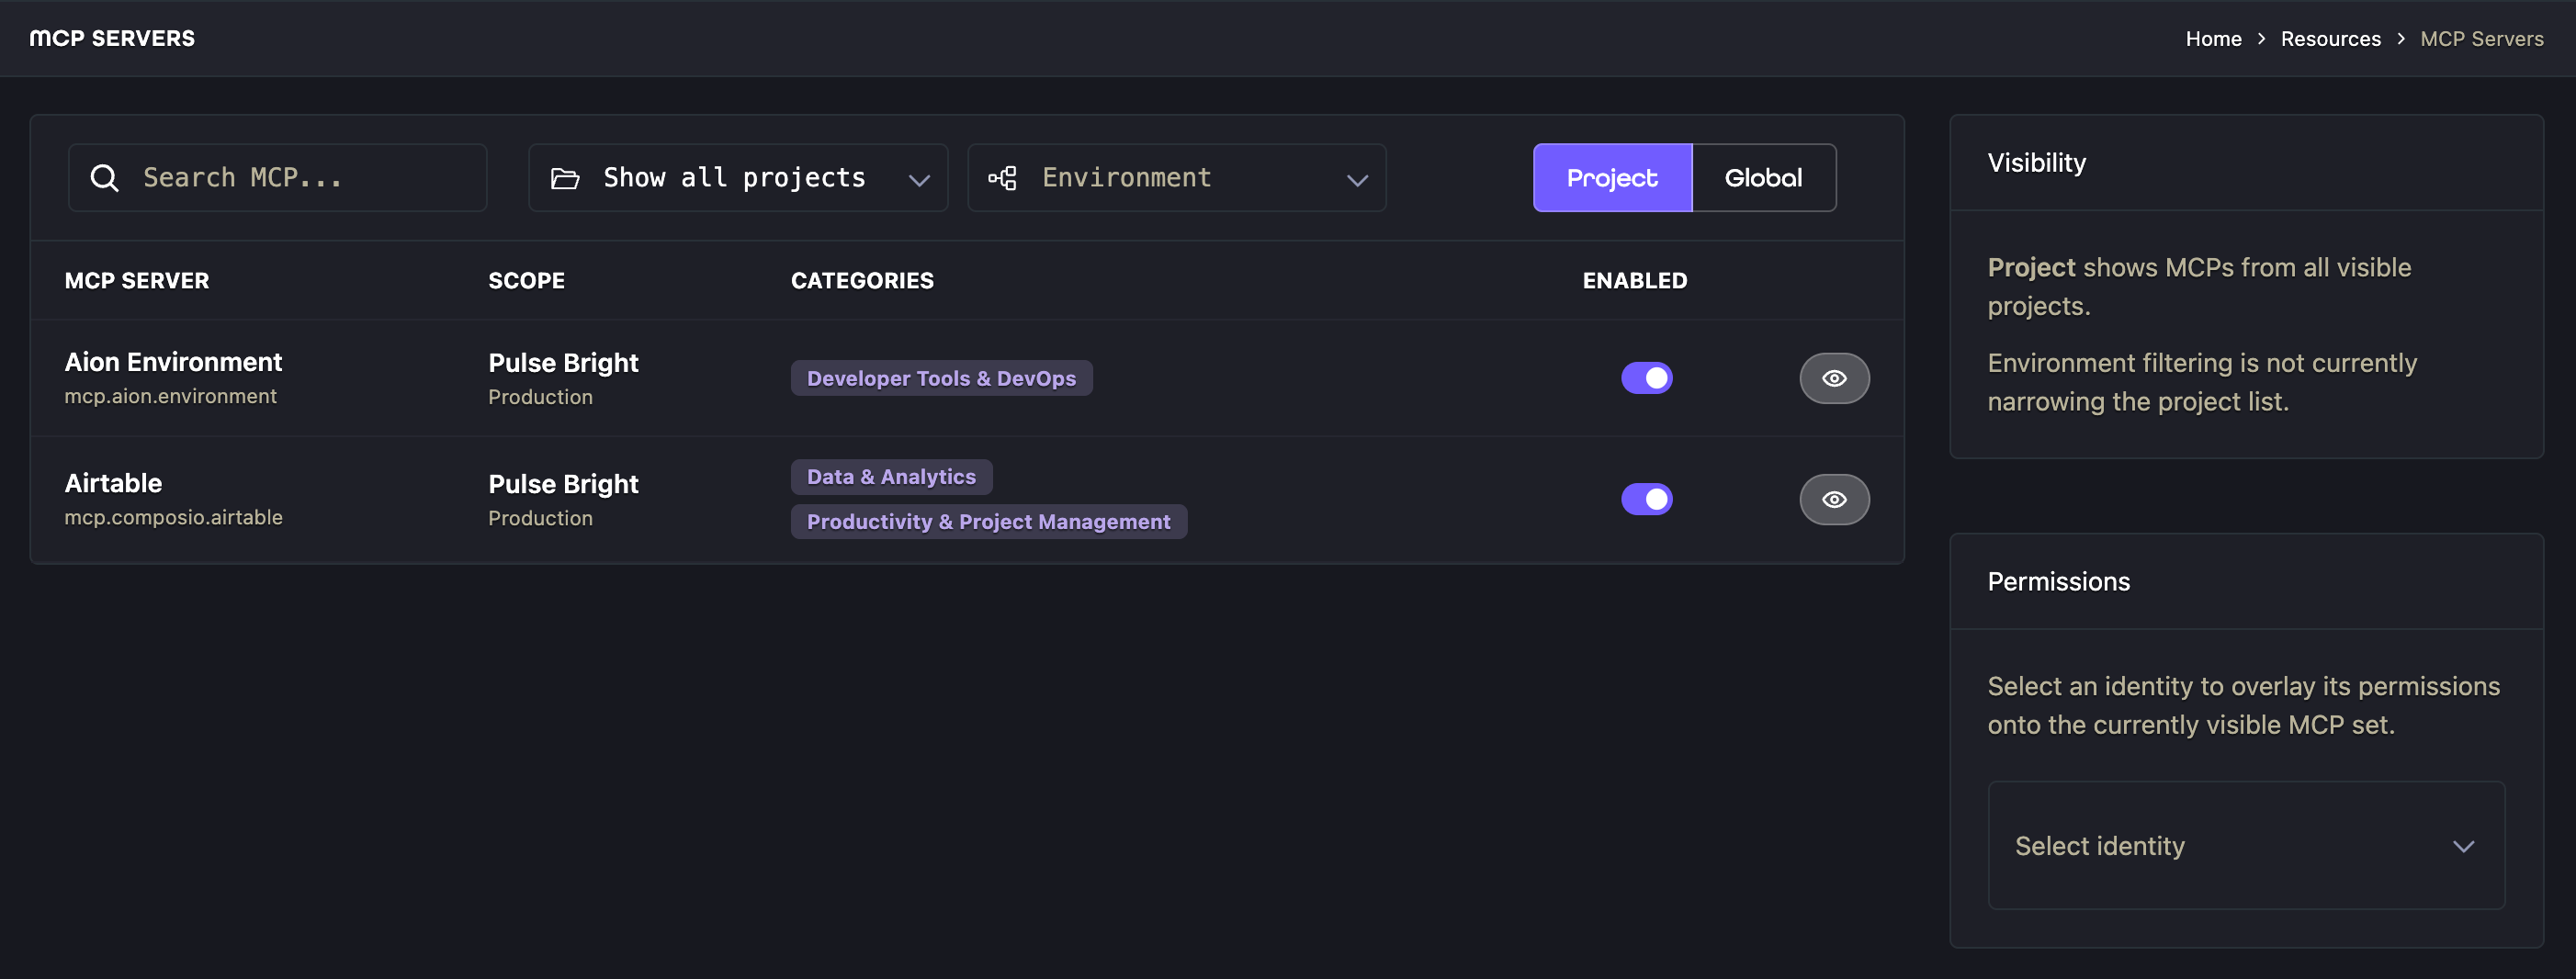
Find a Project MCP server
- Open Resources > MCP Servers. The Project tab opens by default.
- Choose a Project, or select Show all projects.
- Optionally choose an Environment, or select Show all environments.
- Use Search MCP… to filter the visible servers.
- Select View MCP server to open a server’s details.
Preview permissions for an Identity
Select a Personal, Principal, or Daemon Identity in the Permissions card to preview whether its assigned roles include the permissions listed by each server. This preview does not grant access or execute a request. It highlights missing permissions and moves closer matches higher in the results. See Aion Meta Tools for programmatic discovery and environment filtering, and Roles & Permissions for the permissions behind this preview.Enable a global MCP server
- Open the Global tab.
- Find the MCP server you want to use.
- Turn on Enabled.
- Wait for confirmation that the server is enabled.
Authentication
Choose credentials based on where the MCP client runs:OAuth for interactive clients
Use OAuth with interactive MCP clients such as Codex and Claude Code. Each Aion MCP endpoint publishes the authorization information the client needs. After you add the server, the client opens Aion sign-in and uses the resulting authorization when it connects. OAuth acts as the signed-in user. The servers and tools available to the client are limited by that user’s organization membership, visibility, and permissions.Personal API keys
Use a personal API key when a user-operated client cannot complete OAuth or when you need non-interactive access. Create and revoke keys from Settings > Personal > API Keys, then export the key without putting its value in a client configuration:.mcp.json and expand the environment variable in the request header:
Deployment client credentials
Aion deployments useAION_CLIENT_ID and AION_CLIENT_SECRET:
- Remote Deployment: Aion displays both values after you create the deployment. Copy them immediately and add them to the runtime’s environment. The client secret is shown only once and cannot be retrieved later.
- Aion GitHub: Aion injects both values into the hosted runtime environment automatically.
Permissions and attribution
OAuth and personal API-key connections are authorized as their users. A deployment connection authenticates with its Version bearer. Aion verifies forwarded usage attribution and authorizes its executor, or resolves the deployment’s current daemon for direct and autonomous calls. The retiredAion-Principal-Selector header is not accepted.
Use the selected server’s Required Permissions list as the source of truth. MetaTools uses the same authentication
paths and applies the caller’s visibility and permissions when it searches for or executes tools.
Execution permission and usage attribution are separate. A distribution request retains its receiving agent and
originator while downstream daemons execute its tools. Direct deployment work uses the deployment daemon and payer.
See Identities and
Runtime callbacks for these roles and headers.
Usage
Open Resources > MCP Servers, select a server, and open Usage. The page generates the exact endpoint and capability reference for the selected server.Choose an access pattern
Direct server examples target the selected server. MetaTools examples target Aion’s global MetaTools server
and use
aion_tool_search and aion_tool_execute to find and call eligible tools.
Choose a client
Connect an OAuth client
Copy the generated MCP URL into your client configuration. For Codex, the generated example follows this shape:/mcp inside Claude Code to complete authentication.
Connect an Aion deployment
Choose SDK, SDK / LangGraph, or SDK / Google ADK, then copy the generated example. It includes:- the exact capability reference for the selected server;
- an authenticated MCP endpoint;
- the runtime context used to forward signed usage attribution or report a direct caller.
Inspect tools
Open a server to review its summary and tools:
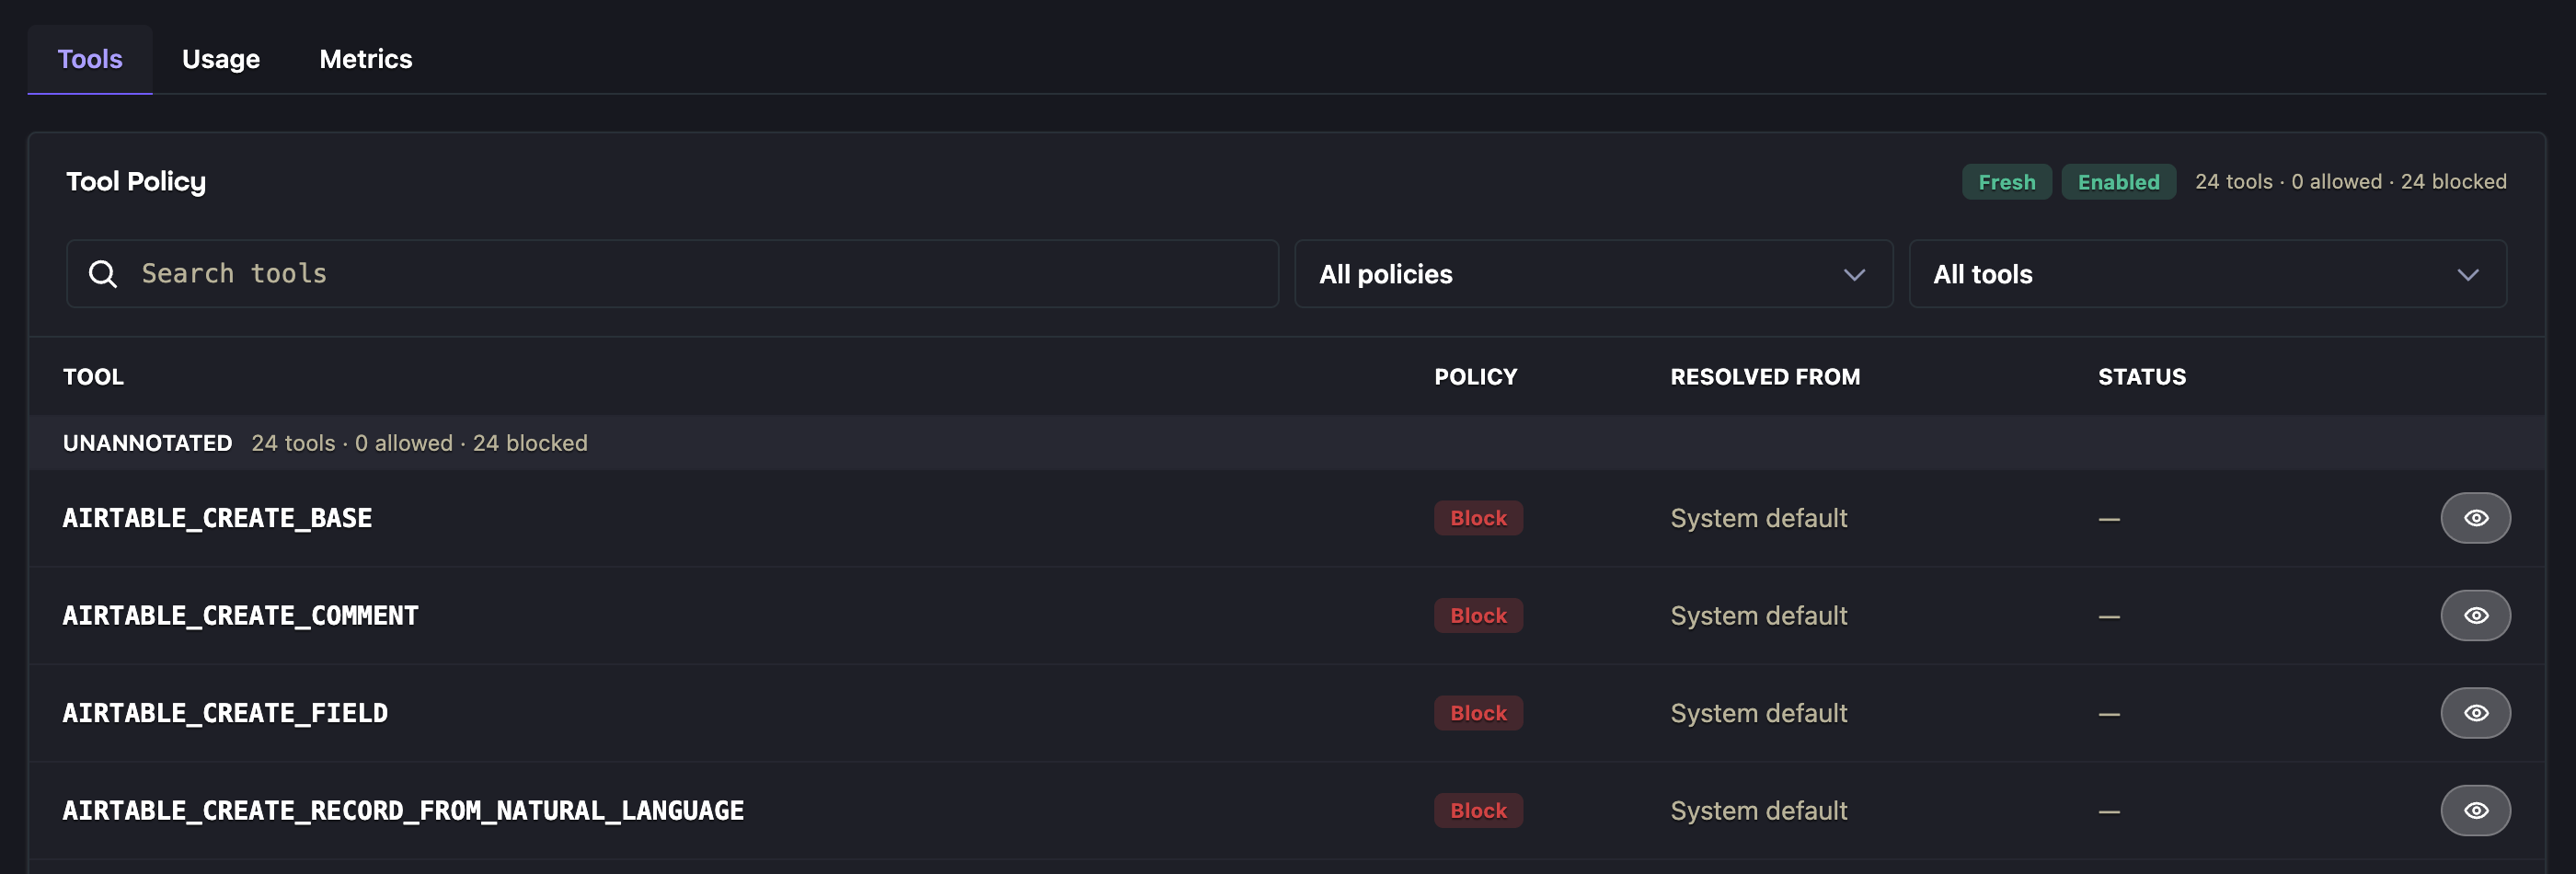
The Tools tab groups tools as read-only, mutating, destructive, or unannotated. Its policy controls are
informational; edit tool policy from the corresponding Ion in Composer.
This example shows an Airtable server whose unannotated tools resolve to Block under the system default:
Monitor usage and cost
Open a server and select Metrics to inspect Credits Used, Principal Attribution, and usage categories. Use the reporting-period control to change the time range.Troubleshoot a connection
Aion Meta Tools
Useaion_tool_search to find tools within an authorized scope, then aion_tool_execute to call a selected result.
Search returns the references needed for execution; it does not grant permission to invoke the tool.
The target’s execution permissions, availability, and tool policy are checked when the call runs.
Resource discovery and environment boundaries
Choose a Project or organization scope that matches the task. Project-scoped access limits discovery to the permitted Project and configured Ions. The Project Agent role does not make every Project in the organization visible. Cross-project discovery requires broaderCapabilityList authority, such as an organization-level grant, or explicit
grants for the relevant Projects. User-operated discovery also respects the user’s visible Projects.
For organization-scope searches by an Agent Identity, Aion normally derives an environment name from its bound Project.
It selects authorized Projects with that same name, ignoring case. For example, a runtime bound to Production
can find eligible resources in another Production Project only when its permissions include that Project.
Matching names alone do not establish access.
An explicit environmentName overrides the derived filter. It can select Development when that is intended, but
cannot expand the caller’s permissions. If no unique environment can be derived, supply the intended environment
explicitly rather than assuming organization access will search every environment.
Eligible global MCP servers are separate from Project resources. They are not selected by Project environment names.
Their discovery still requires the applicable capability-list authority and organization enablement; execution has
its own permission checks. There is no all-organizations search scope.
What to do next
- Follow the LangGraph MCP guide to load MCP tools in a LangGraph application.
- Follow the Google ADK MCP guide to use MCP tools with an ADK agent.
- Review Aion MCP for lower-level client integration.
- Read Identities and Roles & Permissions for access and visibility rules.